
Trust is not a value we hang on a wall. It is the thing every system we build is ultimately selling, and it is the first thing a bank has to extend to a supplier before anything else can happen.
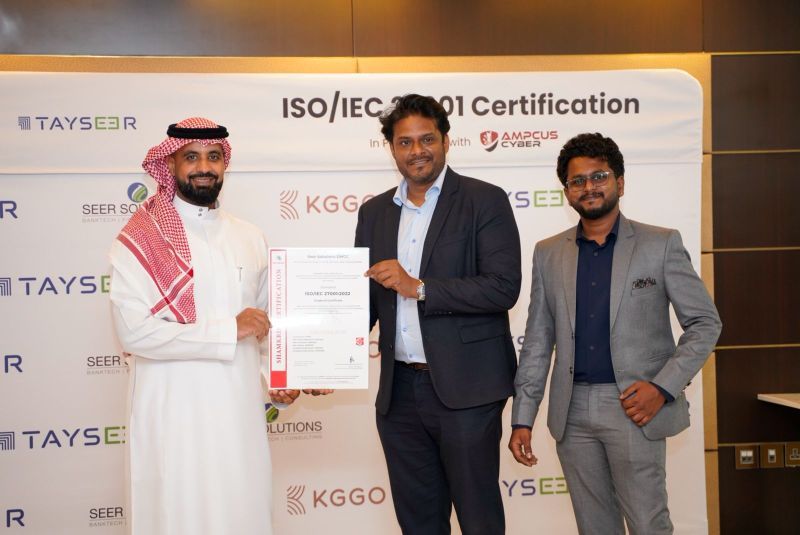
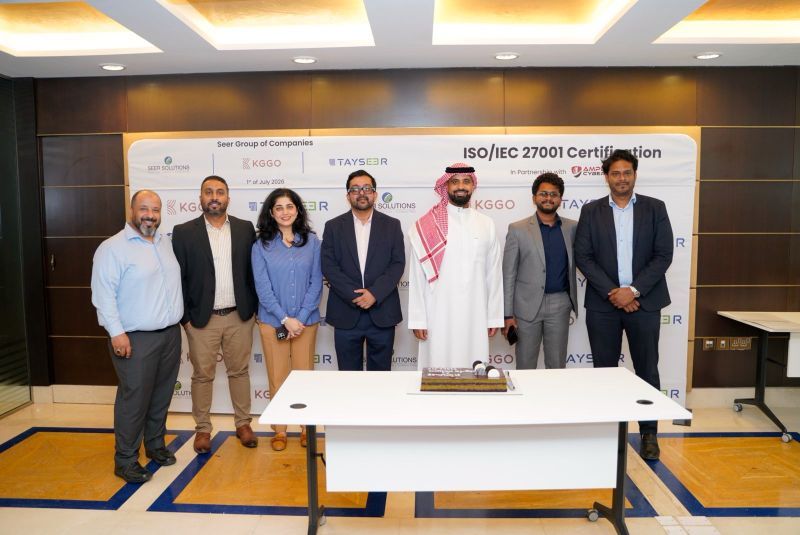
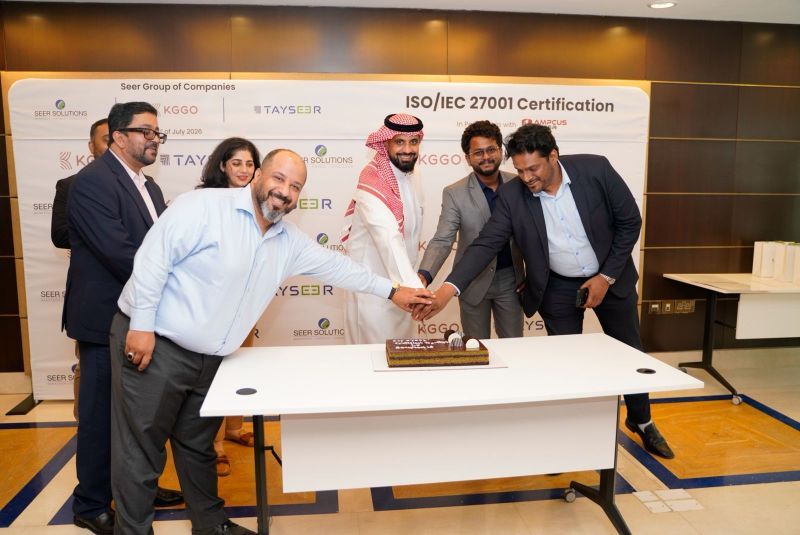
So we are glad to say that Tayseer Innovations has achieved ISO/IEC 27001:2022 certification — the globally recognised standard for information security management — audited independently by Ampcus Cyber, alongside SeerSolutionz and KGGO.
What was actually assessed
ISO/IEC 27001 is often reported as though it were a badge. It is closer to an examination of whether an organisation can demonstrate, on evidence, that it manages information security as a system rather than as a set of good intentions.
The audit covers how risks are identified and treated, how access is granted and revoked, how changes reach production, how incidents are detected and handled, how suppliers are assessed, and — critically — whether any of that survives contact with a normal working week.
Two details are worth stating plainly, because they are the ones that get blurred elsewhere:
It is the 2022 revision. The standard was substantially restructured in 2022, consolidating and modernising its controls. A certificate against an earlier edition is not the same assessment, and we would rather be specific than let the year go unmentioned.
It was audited independently. Ampcus Cyber conducted the assessment. We did not certify ourselves, and no part of this is a self-declaration.
Why it matters more here than elsewhere
We build core ledgers, wallets that hold customer balances, and the monitoring layer over self-service estates that handle physical cash. The blast radius of a security failure in that work is not our reputation — it is somebody’s money, and somebody else’s regulator.
Financial institutions are right not to take a supplier’s word for any of this. Certification does not make a system safe on its own; nothing does. What it provides is an independent, repeatable check that the practices we claim to follow are the practices we actually follow, verified by someone with no stake in the answer.
Credit where it belongs
This kind of certification is not won by a compliance function working alone. It is the accumulation of a great many small decisions made correctly by people who could have made them quickly instead — over months, mostly without an audience.
Our thanks go to our CEO, Mohammed Alkuraimi, and to every member of the team whose work made it possible. The certificate is the visible part. The habits underneath it are the point.